Preparing Business for Q-Day: The Threat of Quantum Computing to Cryptographic Trust
Read more
TechCentral
techcentral.co.za

Preparing Business for Q-Day: The Threat of Quantum Computing to Cryptographic Trust

Every large organization possesses something extremely valuable that remains obscure to many people—this is cryptographic trust. It allows companies to process billions of funds through online banking, manage cloud contact centers, and even authenticate remote employees worldwide. However, the concept of 'Q-Day' has the potential to radically change this situation.

Quantum computing represents an advanced field based on the principles of quantum physics, enabling the solution of complex problems exponentially faster than the world's most powerful supercomputers. Recently, it was noted that China surpassed the best US machines by creating the world's fastest supercomputer. Quantum computers will be able to solve complex mathematical problems, such as cryptographic keys, in mere seconds, whereas the fastest current supercomputers would require trillions of years to crack them.

All of this leads us to the concept of Q-Day—a hypothetical or impending moment when quantum computers become powerful enough to break standard public-key encryption. The question arises: will Q-Day actually happen? Google set a deadline of 2029 for migrating its own systems to post-quantum cryptography. Furthermore, the U.S. government recently called for the development of a quantum computer by 2028.

This means there is a very real risk that quantum computing could devalue or destroy cryptographic trust. But what if it never happens? Naturally, proactive preparation to prevent unpleasant surprises is more important than ignoring the problem in the hope that it is merely science fiction hype.

The uncomfortable truth is that many boards of directors act as if the risk does not exist, while standardization bodies, regulators, and leading technology companies are already working on creating replacements for existing cryptography.

Challenging the Status Quo

Today, when a customer sees a lock icon in a browser or an agent logs into a cloud platform, public-key cryptography is used: two strangers, visible to the internet, agree on a secret key that attackers cannot recover using classical computers. However, a quantum computer with cryptographically significant capabilities completely changes this assumption. What was previously considered secure becomes vulnerable because attackers can realistically extract private keys from public ones, giving them the ability to read or forge protected information.

Companies striving to strengthen their defenses face two different risks. The obvious risk occurs after Q-Day, when attackers gain access to encrypted sessions—for example, between customers and portals, agents and company cloud services, or even internal internet systems—and decrypt them. The second, more insidious risk is already happening. It is called 'Harvest Now, Decrypt Later' (HNDL). Attackers can capture encrypted traffic that they cannot read today and store it cheaply. Then, when Q-Day arrives, yesterday's 'secure' communication becomes tomorrow's leak.

Why Act Now?

Readiness for quantum computing cannot be viewed as a secondary IT project. When the mechanism underlying confidentiality and authenticity—that is, trust—fails, it becomes a governance issue, not just a configuration error. Progress in quantum computing occurs through sudden breakthroughs, such as longer quantum states and more usable qubits. This progress is evident, confirmed by Google accelerating its internal timelines for migration to post-quantum cryptography.

When a company of this scale, managing one of the world's largest cloud environments and developing quantum hardware, accelerates its schedule, boards of directors who dismiss it as 'hypothetical' or 'too early' are playing a dangerous game. Inaction is increasingly becoming an unjustified risk decision. The next generation of cryptographic infrastructure is already being standardized. Bodies such as the U.S. National Institute of Standards and Technology (NIST) have selected and defined post-quantum algorithms: ML-KEM for key establishment, as well as ML-DSA and SLH-DSA for digital signatures. Furthermore, the FIPS 206 standard project is under development and close to final approval, which deeply integrates these ideas into the formal security stack.

These are the basic elements that vendors will use when offering 'quantum-resistant' products. Business leaders do not need to know all the details of these elements, but they must understand that their existence signifies: the industry has moved from the question of 'if' to the question of 'how fast'. The EU's Digital Operational Resilience Act (DORA) is not 'quantum regulation,' but it requires financial institutions and their critical service providers to understand where and how they rely on cryptography. It obligates them to prove their ability to maintain resilience when threat or technology models change.

What can organizations do right now? One practical step is to demand a cryptographic bill of materials, which is a brief map of where the business relies on public-key cryptography for critical functions such as customer login, payment flows, API gateways, and remote access. Without this clear visibility, any talk of a 'quantum strategy' is pure guesswork.

Cloud communications and contact centers are at the intersection of the organization's most sensitive interactions with customers and the public internet. When choosing suppliers, companies hand over a significant part of their cryptographic protection. It is no longer enough to ask only about uptime and features; businesses should ask suppliers of unified communications whether they can rotate certificates at scale, how they reduce token lifetimes, and how they plan to implement post-quantum standards like ML-KEM and ML-DSA as the ecosystem develops.

The exact date of Q-Day will only become clear in hindsight, likely due to a breach or a quiet but urgent update to standards. It may never come. Nevertheless, boards of directors who view readiness for quantum computing as part of their broader duty to protect digital trust will, at least, ensure robust protection if everything turns out to be theoretical, and will have a convincing answer and line of defense if Google and others were right. The rest will be left explaining why they waited for an invitation to a meeting that never came.
Similar stories

First quantum computers arrive in Brazil, marking an advance in national scientific research
Read more
olhardigital.com.br

First quantum computers arrive in Brazil, marking an advance in national scientific research

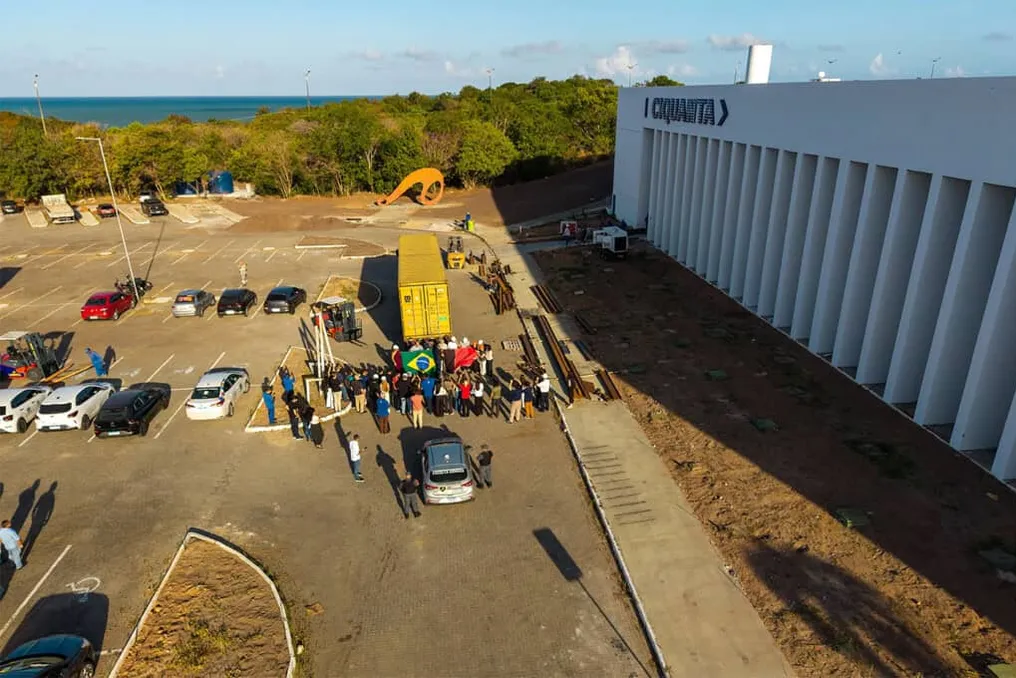
The first quantum computers from Latin America were introduced in Brazil on Monday, the 16th, representing a significant progress for local scientific investigation. These equipment, manufactured in China, will be installed in João Pessoa, Paraíba, giving access to this technology to Brazilian researchers, something previously limited to a few nations.

This initiative covers more than just operating the machines; it includes technology transfer and professional training, aiming to enable Brazil to develop its own quantum computers.

The machines will be housed at the International Center for Computing and Quantum Technologies of Paraíba (Ciquanta), located in the building of the former Arts Station. With an estimated state contribution of around R$150 million, the project aims to connect universities, companies, and research centers to an area with potential to generate innovations in medicine, industry, energy, and digital security.

The fundamental distinction lies in the data processing unit. While traditional computers operate with bits, which represent only zero or one, quantum computers use qubits. Qubits have the ability to manifest a combination of these states, a characteristic called quantum superposition.

Another crucial concept is entanglement, which creates correlations between qubits. Such properties enable the development of calculation methods distinct from those used by conventional machines, offering potential to solve certain categories of problems with greater efficiency.

It is important to note that a quantum computer is not inherently faster in all tasks nor does it replace current equipment. According to the State Secretariat of Science, Technology, Innovation, and Higher Education of Paraíba (Secties), its superiority lies in specific uses, especially those involving complex simulations and a vast range of possibilities.

In the medical and pharmaceutical industry, for example, the technology will assist in simulating molecular behavior and discovering new substances. In the logistics sector, it can optimize routes. Furthermore, energy, agribusiness, climate, and finance are priority sectors for Ciquanta.

Digital security represents another vital aspect. Highly advanced quantum computers can compromise certain current encryption systems. For this reason, researchers also need to focus on developing post-quantum cryptography, specifically created to shield information against such threats.

Quantum computers use processors based on superconducting circuits. For these components to function correctly, they must operate at temperatures very close to absolute zero, which corresponds to the theoretical limit of -273.15 degrees Celsius.

The chips require operation near absolute zero to maintain the properties of the superconducting materials used in the processor construction. Claudio Furtado, Secretary of State for Science, Technology, Innovation, and Higher Education of Paraíba and a Doctor of Physics, detailed the process in an interview with Olhar Digital. He explained that cooling is done by dilution, using a mixture of helium-3 and helium-4 with liquid nitrogen, reaching extremely low temperatures.

Furtado added that the chip technology is superconducting and operates around 10 millikelvin to ensure good performance. This temperature range is necessary because the chip is built with Josephson junctions made of superconductors.

He emphasized that thermal control is essential to preserve the quantum states of the processors, as heat can cause the loss of quantum coherence, harming calculations. Thus, the components remain isolated within the cooling system, even if the room's ambient temperature is maintained at approximately 21°C.

The equipment was manufactured by the China Electronic Technology Group Corporation (CETC) and traveled from the Asian country to Pernambuco, disembarking at the Port of Suape. Subsequently, they traveled by road to João Pessoa, under escort and with controlled speed to minimize vibrations during transit.

The secretary justified the choice of the former Arts Station to host the center due to the adequate infrastructure and architectural features favorable for equipment installation, such as the high ceiling, which allows for accommodating the computer niches. The building is being adapted to receive laboratories, support spaces, and researcher rooms.

However, the physical structure is only one part of the project. Collaboration with the Chinese manufacturer includes knowledge transfer on chip design and manufacturing, cryogenics, sensors, maintenance, telemetry, software, and cryptography.

Training of Brazilian professionals has already begun. An initial group participated in an online course and subsequently traveled to China for in-person training, where they are expected to collaborate on equipment assembly with the Chinese team. New groups will be continuously formed.

Furtado clarified that the agreement covers various phases of the technological chain, providing Brazilians with the necessary knowledge to understand the construction and maintenance of the devices. The expectation is that this knowledge will lead to the development of national equipment, which the secretary considers one of the greatest benefits of the initiative. He stated: 'From a technological point of view, we will first have access to and mastery of the entire chain. We are not talking about prototypes, but functional equipment and technology transfer. The next step is to develop new computers right here in Brazil, with the participation of Brazilian researchers from different centers across the country.'

Ciquanta will make the quantum computers available to universities, research institutes, companies, and government agencies. Access will occur through a cloud platform, allowing researchers from various regions of the country to use the equipment remotely, without needing to travel to João Pessoa.

Project selection will be carried out through public calls for proposals and in partnership with entities such as the Financing of Studies and Projects (Finep) and the Association for the Promotion of Brazilian Software Excellence (Softex).

The first actions supported by these institutions will focus on training and technological residency, offering capacity building from fundamentals to advanced knowledge to prepare professionals for quantum computing and technologies.

The center also aims to foster the creation of deep tech—startups that create solutions based on scientific research and complex technologies. The programming will include hackathons, courses, and events involving universities, companies, sectoral associations, and government representatives.

The plan foresees Ciquanta becoming an Autonomous Social Service (SSA) and functioning as a Scientific, Technological, and Innovation Institution (ICT). This structure will allow for expanding funding sources and accessing incentive mechanisms, such as the Bem Law and the Informatics Law.

The assembly of the computers is scheduled to begin on Tuesday, the 24th, with an expected completion by the end of December, after which the equipment will undergo testing and validation. The first research is planned to start in the first semester of 2027.

While the adaptations of Ciquanta continue, the project is already promoting activities to familiarize the public with quantum computing. A full-scale replica of the computers is on display at the Technological Park, in the Historic Center of João Pessoa, offering free guided tours led by researchers.

The arrival of these first quantum computers from Latin America in Brazil signals the opening of a new frontier for national science, integrating this technology into the country's research infrastructure and generating opportunities for Brazilian scientists to investigate complex problems and contribute to future technological transformations.

Cryptography Requirements and the Transition to Quantum-Resistant Security
Read more
yourstory.com

Cryptography Requirements and the Transition to Quantum-Resistant Security

A scenario is emerging where confidential information encrypted and sent many years ago could suddenly be decrypted. Even though security systems were functioning correctly, information was exchanged, and encryption algorithms were considered reliable, no signs of a breach were detected. However, advances in computing have made this previously protected information vulnerable. It is this problem that is stimulating the discussion on quantum-resistant security.

Encryption is used to protect virtually every aspect of our digital lives. The encryption algorithms we use to protect sensitive data, such as banking transactions, medical records, industrial communications, and defense systems, have been trusted for decades. Nevertheless, the advent of quantum computing calls into question our assumptions about how long certain types of security will remain effective.

Although quantum computers capable of breaking popular public-key cryptography are currently unavailable, the possibility of their emergence is a critical factor for organizations needing to ensure long-term data security.

Modern cybersecurity relies on various types of cryptography for different purposes. The Advanced Encryption Standard (AES) algorithms are used to protect data. Public-key cryptography, such as RSA and Elliptic Curve Cryptography (ECC), is applied to ensure authentication, key establishment, and digital signatures.

Quantum computing poses several challenges to these cryptographic systems. With Shor's algorithm, a sufficiently powerful quantum computer can theoretically solve the mathematical problems underlying RSA and ECC, thereby compromising systems dependent on them. Regarding Grover's algorithm, it provides a theoretical speedup in searching keys in symmetric encryption. For AES-256, this reduces the theoretical margin of safety against brute-force attacks, but it does not make AES-256 practically breakable using current quantum computing capabilities. It is important to understand exactly which cryptographic systems are at the highest risk before determining what needs to be changed.

Another issue is that attackers can collect encrypted information today and store it for later decryption. This approach is called 'harvest now, decrypt later' and poses a risk to information that must remain protected for many years. Confidential defense communications, financial data, and intellectual property can retain their value long after initial transmission.

While replacing an encryption algorithm may seem like a simple task, the digital infrastructure we use today consists of numerous interconnected systems with varying security needs. For example, consider an industrial facility with hundreds of connected sensors, controllers, and communication devices. Some of these devices might have been installed many years ago and could be used for another decade. Others may have limited computational power, memory, or network connectivity. The timing of implementing new cryptographic mechanisms in such systems must be carefully considered.

Using post-quantum cryptographic algorithms may require larger key sizes, signatures, or more computational power compared to existing public-key cryptography mechanisms. These differences can affect communication bandwidth, memory usage, and processing performance. For real-time devices, any changes in computational requirements can impact system design. Therefore, the entire security architecture, including device authentication, key management, communication protocols, and hardware compatibility, must be taken into account. This is not just about updating software for quantum resistance.

We are beginning to see a shift towards post-quantum cryptography. The U.S. National Institute of Standards and Technology (NIST) approved three post-quantum cryptography standards in August 2024: ML-KEM for key establishment, and ML-DSA and SLH-DSA for digital signatures. These standards provide organizations with specific cryptographic mechanisms designed to counter attacks from both traditional and quantum computers. However, implementing these standards is not merely replacing cryptographic algorithms.

It is necessary to identify the vulnerable cryptography we are using, understand how encryption keys are generated and exchanged, and assess whether existing systems can support these requirements. Alternative approaches, such as out-of-band key distribution and quantum key distribution, are also being studied. These methods offer different security properties but come with practical considerations such as infrastructure, cost, scalability, and compatibility.

There is no one-size-fits-all solution that meets all operational requirements. The correct architecture depends on the sensitivity of the information, the devices involved, and the environment in which the communication takes place.

One of the most crucial steps organizations can take to prepare is establishing cryptographic agility. This implies developing systems capable of adapting to changes in cryptographic algorithms and protocols without major infrastructure overhauls. Firstly, organizations must understand their cryptographic dependencies: which algorithms are used, where keys are stored, how devices are authenticated, and which systems might be difficult to update. Secondly, prioritization is necessary: systems protecting long-lived sensitive information or critical infrastructure may require earlier migration planning.

Employing hybrid cryptographic approaches (simultaneously using existing classical mechanisms and post-quantum cryptographic algorithms) can help manage the transition process while maintaining compatibility during migration. For connected and embedded systems, security must also be considered during hardware and software design. Devices expected to be in operation for many years must support secure updates and be adaptable to changing cryptographic mechanisms, where technically feasible.

The transition to quantum-resistant security will be a gradual process. Given existing infrastructure, operational constraints, and evolving standards, organizations will need to meticulously plan migration strategies. This is particularly challenging for sectors such as banking, telecommunications, manufacturing, and defense, where sensitive information and long-lived connected infrastructure are common. It is not necessary to wait until quantum computing poses an immediate threat to begin preparation; information encrypted today may need protection for decades. Systems deployed today may be used long after cryptographic requirements have changed. The main focus should be on understanding current vulnerabilities, studying new standards, and creating adaptive systems for the changing landscape of cryptographic technologies. The future of cybersecurity will depend equally on the ability to update and maintain trusted security as it will on the strength of the encryption algorithms used.

Uttar Pradesh plans to launch its own quantum mission and establish deep technology centers in Noida and Lucknow
Read more
www.aajtak.in

Uttar Pradesh plans to launch its own quantum mission and establish deep technology centers in Noida and Lucknow

The state of Uttar Pradesh is working to strengthen its presence in the field of emerging technologies, under which the state government plans to launch a specialized state quantum mission. The goal of this initiative is to stimulate research, innovation, and technological capabilities in the field of quantum computing and related technologies.

This proposed mission was announced by Alok Kumar, Chief Secretary of the Department of Information Technology and Electronics of Uttar Pradesh, during the ETGovernment AI Vision Conclave held in Lucknow in October 2026. Simultaneously, work is underway to create U-Hubs in Noida and Lucknow to develop the deep technology ecosystem in the state.

In August 2026, the Uttar Pradesh cabinet approved the creation of these two centers. According to the Uttar Pradesh Startup Mission, the center in Noida will focus on advanced technologies such as quantum and advanced computing, semiconductor design, robotics, and defense technologies. Meanwhile, the center in Lucknow will focus on applied artificial intelligence (AI), medical technologies, GovTech, and other emerging technology areas.

These centers are envisioned as platforms to facilitate collaboration between startups, research institutions, and industry. It is planned that through them, startups will gain access to incubation, mentorship, and technical resources.

The Uttar Pradesh initiative aligns with the Central Government's National Quantum Mission. In April 2023, the central government approved this mission with a budget of ₹60,03.65 crore for the period 2023-24 to 2030-31. Its objective is to promote research and development in the fields of quantum computing, quantum communication, quantum sensing, and metrology, as well as quantum materials and devices.

Thanks to the proposed quantum mission and deep technology centers, Uttar Pradesh is moving forward in strengthening its research and innovation ecosystem and encouraging the development of new technologies.

Popular