Outlook presents instability and hinders access to email inboxes
Read more
Tecnoblog
tecnoblog.net

Outlook presents instability and hinders access to email inboxes

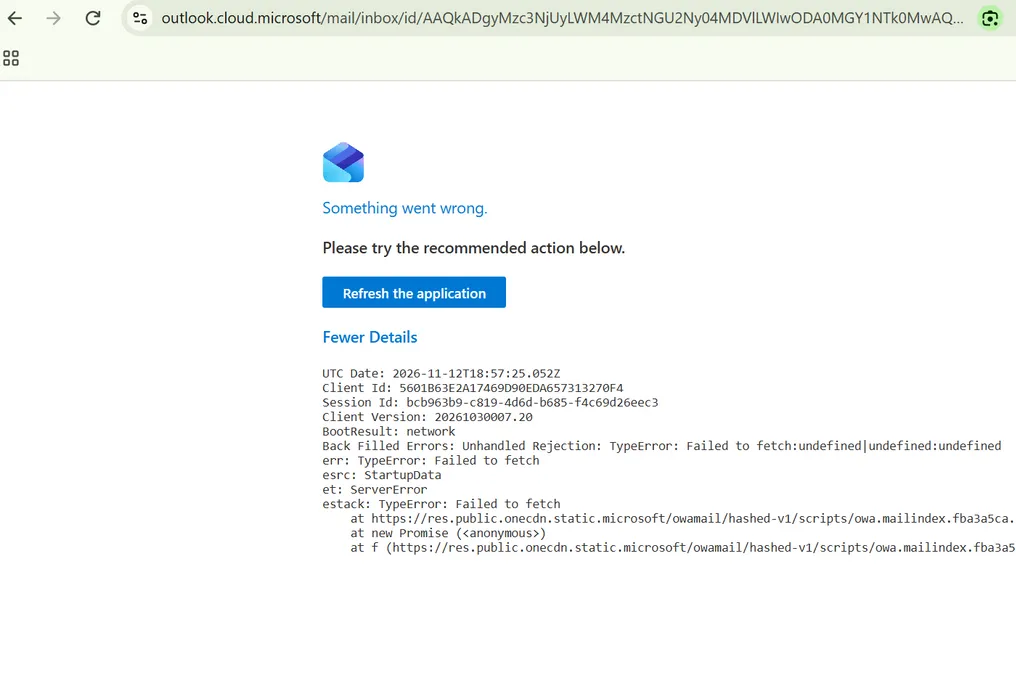
The Outlook service is experiencing instability this Thursday, November 12th, which has complicated users' access to their email inboxes. Microsoft confirmed that it is conducting an investigation into connection issues in Exchange Online, a service integrated with Microsoft 365.

According to the company itself, the failure may be caused by an overload in parts of the infrastructure across various regions. Although the first reports of problems were noted in the Americas, there is a possibility that users in any other area may also be affected.

Microsoft is actively working to reduce the impact of this situation and provides updates in the Microsoft 365 admin center, using codes EX1550543 and MO1550821. Regarding initial reports, it was mentioned that the company was investigating access issues to Exchange Online mailboxes through multiple connection methods in the Americas.

On online service monitoring platforms, such as DownDetector, the registration of user complaints began to increase around 2:45 PM on the current day.

Similar stories

Microsoft Outlook and Microsoft 365 Servers Fail Worldwide; Over 100,000 Complaints Registered
Read more
www.aajtak.in

Microsoft Outlook and Microsoft 365 Servers Fail Worldwide; Over 100,000 Complaints Registered

The workflow of millions of offices worldwide suddenly stopped on Thursday due to a failure in the email service servers for Outlook and the Microsoft 365 service from technology giant Microsoft. This technical glitch caused difficulties for thousands of users when sending, receiving emails, and logging into their accounts.

According to the DownDetector platform, which tracks the status of online services, the issue with Outlook began around 1 PM Eastern Time. Soon, the number of complaints sharply increased, peaking when over 100,000 messages related to Outlook were registered.

Similarly, more than 15,000 users reported problems with Microsoft 365. Microsoft confirmed this outage on the social network X and stated that its team was investigating the situation.

Initially, it seemed the problem was limited to the US, but later the company admitted that its impact could be global. Microsoft stated: 'While we work to mitigate the impact, we confirm that this issue may affect connectivity to Microsoft 365 services for users in any region.'

The company specified that an excessive load increased on part of its infrastructure in several regions, leading to connection issues. To balance the load, Microsoft began redistributing network traffic across its global infrastructure.

During this outage, the Microsoft status page (status.cloud.microsoft), which was supposed to provide information, also encountered a loading error. Nevertheless, the company notified users about the possibility of receiving updates through the Admin Center using codes EX1550543 and MO1550821. At the time of publication, engineers continued to work on a full resolution of the issue.

Microsoft Outlook presents instability on Thursday, the 12th
Read more
olhardigital.com.br

Microsoft Outlook presents instability on Thursday, the 12th

On Thursday afternoon, the 12th, Microsoft Outlook began to show operational problems. The failures range from the ability to log in to the platform to the processes of sending and viewing email messages.

The Downdetector platform, used to monitor the status of online services, registered a volume of complaints close to two thousand cases. Furthermore, complaints were noted about the situation on social media in various global regions.

On X, users worldwide reported difficulties with the service. Despite the issues identified by the public, Microsoft itself states on its status page that Outlook remains operational. To date, the company has not issued an official statement regarding the incident.

Exploit in Microsoft Outlook allows hackers to capture Windows credentials
Read more
olhardigital.com.br

Exploit in Microsoft Outlook allows hackers to capture Windows credentials

A vulnerability in Microsoft Outlook could potentially expose the authentication information of Windows users. This vulnerability, identified as CVE-2026-124194, was already being exploited by attackers before Microsoft released fixes on Tuesday (the 10th).

This issue allows intruders to obtain the NTLMv2 authentication hash, which can then be used in attempts to access systems and accounts by impersonating a legitimate user. To exploit this flaw, an attacker must convince the victim to open a specially prepared message file.

Microsoft classified this vulnerability as moderate, but confirmed active instances of its use. Furthermore, the US Cybersecurity and Infrastructure Security Agency (CISA) included this vulnerability in its catalog of known exploited vulnerabilities.

The fix was released on Tuesday (the 10th) as part of Microsoft's monthly security update package, known as Patch Tuesday. The company confirmed that CVE-2026-124194 was exploited prior to the patch's availability. The vulnerability was defined as a spoofing error with a CVSS score of 6.5, which measures the severity of digital security issues.

The official advisory states that affected products include Microsoft 365 Apps for Enterprise, as well as Office LTSC 2021 and Office LTSC 2024 versions. The discovery was attributed to researchers named Nono and Benoît Sevens. According to Microsoft, Sevens utilized Claude, an artificial intelligence (AI) model from Anthropic, during the vulnerability analysis process.

CISA also added this flaw to its catalog of known exploited vulnerabilities, known as KEV. The agency set a deadline of November 24, 2026, for US federal civilian agencies to apply the fix. This requirement is directed at American institutions, not Brazilian companies.

The Outlook vulnerability is part of a larger set of updates provided by Microsoft in November. According to the analysis, the package includes 1,259 fixes and vulnerability identifiers. Of this total, 1,094 relate to Microsoft's own product flaws, while 165 other identifiers were published based on third-party reports.

Among the covered products are Windows and Office. The package contains 726 fixes related to Windows and 174 related to Office, in addition to over 500 privilege escalation vulnerabilities—a situation where an attacker gains higher permissions than intended in a specific system. The update also addresses errors that could allow remote code execution in Windows components, and a privilege escalation vulnerability in Azure OpenAI.

This marks the second consecutive month that Microsoft's monthly security package has exceeded one thousand vulnerabilities. The article about the Outlook breach first appeared on the Olhar Digital portal.
Popular